
Cisco · Network Switch
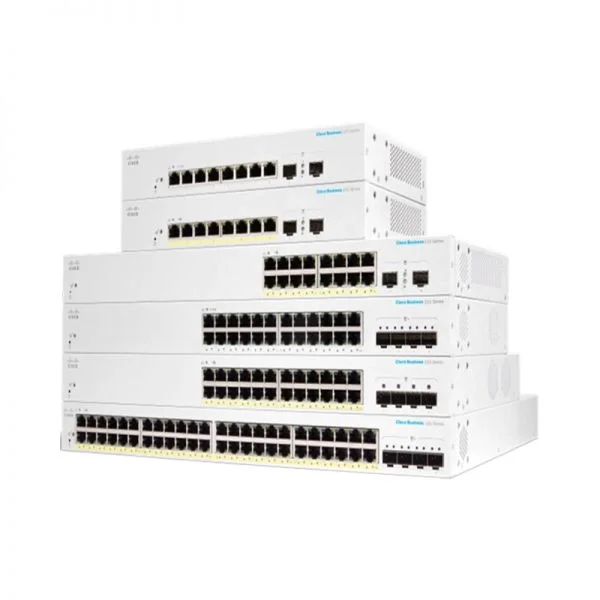
Cisco CBS220-24P-4G Cisco CBS220-24P-4G - Cisco Business 220 Series Smart Switches 24 10/100/1000 ports with 1…
Model: CBS220-24P-4G|Condition: Original Used|Warranty: 3 months
The Cisco CBS220-24P-4G is stocked by ImportGM for resellers, MSPs and enterprise buyers sourcing genuine network switches with export-ready documentation. From connectivity to cloud applications, networking plays a crucial role in every business journey. Reliability, security, and affordability continue to be priorities, while ongoing management and operations add additional complexity that takes time and resources. Core parameters include switching capacity Model name. Original Used units carry the 3 months ImportGM warranty; quotation, proforma invoice and export packing list are issued the same day.
- ✔Cisco CBS220-24P-4G Specification
- ✔24 10/100/1000 ports with 195W power budget, 4 Gigabit SFP
- ✔Cisco Business 220 Series Smart Switches
- ✔Prominent feature
- ✔Business Applications
- ✔Features and benefits
Bulk pricing available · Export packing & documentation · DHL / FedEx / air / sea freight
Technical Specifications
| Feature | Description |
|---|---|
| Switching capacity | Model name |
| CBS220-8T-E-2G | 14.88 |
| CBS220-8P-E-2G | 14.88 |
| CBS220-8FP-E-2G | 14.88 |
| CBS220-16T-2G | 26.78 |
| CBS220-16P-2G | 26.78 |
| CBS220-24T-4G | 41.66 |
| CBS220-24P-4G | 41.66 |
| CBS220-24FP-4G | 41.66 |
| CBS220-48T-4G | 74.38 |
| CBS220-48P-4G | 74.38 |
| CBS220-24T-4X | 95.23 |
| CBS220-24P-4X | 95.23 |
| CBS220-24FP-4X | 95.23 |
| CBS220-48T-4X | 130.94 |
| CBS220-48P-4X | 130.94 |
| CBS220-48FP-4X | 130.94 |
| MAC table | Up to 8,192 Media Access Control (MAC) addresses |
| Spanning Tree Protocol (STP) | Standard 802.1d Spanning Tree support, enabled by default Fast convergence using 802.1w (Rapid Spanning Tree [RSTP]) Multiple Spanning Tree instances using 802.1s (MSTP) 16 instances are supported |
| Port grouping | Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) ● Up to 8 groups ● Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation Load balance based on source and destination MAC address, or source and destination MAC/IP |
| VLAN | Support for up to 256 Virtual Local Area Networks (VLANs) simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN |
| Auto voice VLAN | Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS |
| QinQ VLAN | VLANs transparently cross a service provider network while isolating traffic among customers |
| Head-of-Line (HOL) blocking | HOL blocking prevention |
| Jumbo frame | Frame sizes up to 9,216 supported |
| Loopback detection | Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP. |
| Automatic Media-Dependent Interface Crossover (MDIX) | Automatically adjusts transmit and receive pairs if an incorrect cable type (crossover or straight-through) is installed. |
| ACLs | Drop or rate limit based on source and destination MAC, VLAN ID or IP address, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, Transmission Control Protocol (TCP)/ User Datagram Protocol (UDP) source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, Internet Group Management Protocol (IGMP) packets, TCP flag Support up to 512 rules |
| Port security | Creates the ability to lock source MAC addresses to ports; limits the number of learned MAC addresses |
| IEEE 802.1X (authenticator role) | 802.1X: Remote Authentication Dial-in User Service (RADIUS) authentication; guest VLAN; Single-host, multiple-host, and multisession mode |
| RADIUS, TACACS+ | Supports RADIUS and Terminal Access Controller Access Control System (TACACS) authentication; switch functions as a client |
| MAC address filtering | Supported |
| Storm control | Broadcast, multicast, and unknown unicast |
| DoS protection | DOS attack prevention |
| STP Bridge Protocol Data Unit (BPDU) Guard | This security mechanism protects the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. |
| Spanning Tree Loop Guard | This feature provides additional protection against Layer 2 forwarding loops (STP loops). |
| Secure Shell (SSH) Protocol | SSH is a secure replacement for Telnet traffic. SCP also uses SSH. SSH v1 and v2 are supported. |
| Secure Sockets Layer (SSL) | SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch |
| Priority levels | 8 hardware queues per port |
| Scheduling | Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS) |
| Class of service | Port-based; 802.1p VLAN priority-based; IPv4/v6 IP precedence, Type of Service (ToS), and DSCP-based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS |
| Rate limiting | Ingress policer; egress shaping and rate control; per VLAN, per port, and flow-based |
| Congestion avoidance | A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization. |
| Internet Group Management Protocol (IGMP) Versions 1, 2, and 3 Snooping | IGMP limits bandwidth-intensive multicast traffic to only the requesters; supports 256 multicast groups |
| IGMP querier | IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router |
| Standards | IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad LACP, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.1D (STP, GARP, and GVRP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, Request for Comments (RFC) 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 922, RFC 920, RFC 950, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1350, RFC 1533, RFC 1541, RFC 1624, RFC 1700, RFC 1867, RFC 2030, RFC 2616, RFC 2131, RFC 2132, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 2576, RFC 4330, RFC 1213, RFC 1215, RFC 1286, RFC 1442, RFC 1451, RFC 1493, RFC 1573, RFC 1643, RFC 1757, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2233, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 1157, RFC 1493, RFC 1215, RFC 3416 |
| IPv6 | IPv6 host mode IPv6 over Ethernet IPv6/IPv4 Dual Stack IPv6 neighbor and router discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 |
| IPv6 ACL | Drop or rate limit IPv6 packets in hardware |
| IPv6 QoS | Prioritize IPv6 packets in hardware |
| Multicast Listener Discovery (MLD v1/2) Snooping | Deliver IPv6 multicast packets only to the required receivers |
| IPv6 applications | Web/SSL, Telnet server/SSH, DHCP Client, DHCP Autoconfig, Cisco Discovery Protocol (CDP), Link Layer Discovery Protocol (LLDP) |
| IPv6 Requests for Comments (RFCs) supported | RFC 4443 (which obsoletes RFC2463) - ICMP version 6 RFC 4291 (which obsoletes RFC 3513) - IPv6 address architecture RFC 4291 - IPv6 addressing architecture RFC 2460 - IPv6 specification RFC 4861 (which obsoletes RFC 2461) - Neighbor discovery for IPv6 RFC 4862 (which obsoletes RFC 2462) - IPv6 stateless address auto-configuration RFC 1981 - Path MTU discovery RFC 4007 - IPv6 scoped address architecture RFC 3484 - Default address selection mechanism |
| Cisco Business Dashboard | Support direct management with Cisco Business Dashboard and mobile app. Eliminates the need to set up a separate hardware or virtual machine for the Cisco Business Dashboard Probe on site. |
| Cisco Business mobile app | Mobile app for Cisco Business Switch and Wireless products. Helps to set up a local network in minutes and provide easy management at your fingertips. |
| Cisco Network Plug and Play (PnP) agent | The Cisco Network Plug and Play solution provides a simple, secure, unified, and integrated offering to ease new branch or campus device rollouts or for provisioning updates to an existing network. The solution provides a unified approach to provision Cisco routers, switches, and wireless devices with a zero touch deployment experience. Supports Cisco PnP Connect |
| Web user interface | Built-in switch configuration utility for easy browser-based device configuration (HTTP/HTTPS). Supports configuration, system dashboard, system maintenance, and monitoring |
| Text-editable config files | Config files can be edited with a text editor and downloaded to another switch, facilitating easier mass deployment |
| Command-line interface | Scriptable CLI; a full CLI is supported. User privilege levels 1 and 15 are supported for the CLI |
| SNMP | Simple Management Network Protocol (SNMP) versions 1, 2c, and 3 with support for traps, and SNMP version 3 User-based Security Model (USM) |
Product Overview
From connectivity to cloud applications, networking plays a crucial role in every business journey. Reliability, security, and affordability continue to be priorities, while ongoing management and operations add additional complexity that takes time and resources.
Cisco Business is a portfolio of affordable wireless access points, switches, and routers designed and built for Small Business. Managed through Cisco Business Dashboard and mobile app, the portfolio provides a simple and reliable experience. Cisco Business Dashboard simplifies traditional challenges in deploying and managing business networks by automating the deployment, monitoring, and lifecycle management of the network.
The Cisco Business 220 Series are affordable smart switches with ease of use, security, and reliability for business-class networks. With intuitive dashboard, Power over Ethernet (PoE) options, and customizable features, these switches deliver a solid business network within your budget parameters. When you need a business-class network and cost is top priority, Cisco Business 220 Series provides an excellent solution.
● Small office networking: The versatility and affordability of the Cisco Business 220 Series family of switches provide an ideal business-class networking foundation for small businesses with limited IT support and budget.
● Wireless connectivity. With PoE+ support, and comprehensive security and Quality of Service (QoS) capabilities, Cisco Business 220 Series switches provide a solid foundation to add business-grade wireless to the network. You can easily deploy Cisco Business wireless access points to increase workforce productivity without worrying about power and throughput.
● Unified communications. The Cisco Business 220 Series switches provide QoS features to automatically prioritize delay-sensitive traffic to help you easily deploy an IP-based communication solution on a converged network. PoE+ support can enable IP cameras and videophones to be easily added to your current network. Cisco offers a complete portfolio of IP telephony and other unified communications products designed for small businesses. Cisco Business 220 Series switches have been rigorously tested to help ensure easy integration and full compatibility with these and other vendor products.
Related Network Switchs
Cisco
C1200-16P-2G
C1200-16P-2G Cisco C1200-16P-2G - Cisco Switches 16x 10/100/1000 PoE+ Ports
Cisco
C1200-16T-2G
Cisco C1200-16T-2G Catalyst 1200 16-port GE, 2x1G SFP 16x 10/100/1000 ports
Cisco
C1200-24FP-4G
Cisco C1200-24FP-4G Catalyst 1200 24-port GE, Full PoE, 4x1G SFP 24x 10/100/1000 PoE+ ports
Cisco
C1200-24FP-4X
C1200-24FP-4X Cisco C1200-24FP-4X - Cisco Switches

Cisco
C1200-24P-4G
C1200-24P-4G Catalyst 1200 24-port GE, PoE, 4x1G SFP 24x 10/100/1000 PoE+ ports
Cisco
C1200-24P-4X
C1200-24P-4X, Cisco C1200 Switch, 24x PoE+ 195W/4x 10G SFP+/Rack-mountable
About Network Switchs from ImportGM
Campus access, aggregation and core switches — PoE+, multi-gigabit and 10G/25G/40G/100G platforms from Cisco, H3C, Alcatel-Lucent, Ruckus, Aruba, Huawei and Fortinet. All units genuine, serial traceable and export ready.
Browse all Network Switchs →