
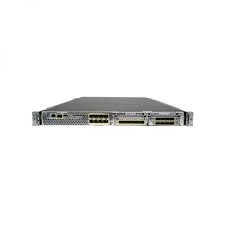
Cisco · Network Firewall
FPR4110-NGFW-K9-RF Cisco Firepower 4100
Model: FPR4110-NGFW-K9-RF|Condition: Original New|Warranty: 1 year
The Cisco FPR4110-NGFW-K9-RF is stocked by ImportGM for resellers, MSPs and enterprise buyers sourcing genuine network firewalls with export-ready documentation. The Cisco Secure Firewall 4100 Series is a family of four threat-focused NGFW security platforms. Their throughput range addresses internet edge, data center and service provider use cases. They deliver superior threat defense, at faster speeds, with a smaller footprint. Core parameters include throughput: fw + avc (1024b) 19 Gbps, throughput: fw + avc + ips (1024b) 19 Gbps. Original New units carry the 1 year ImportGM warranty; quotation, proforma invoice and export packing list are issued the same day.
- ✔Cisco Secure Firewall 4100 Series appliances
- ✔Optional Interfaces
- ✔8 x SFP+ on-chassis
- ✔Detailed performance specifications and feature highlights
- ✔Throughput: FW + AVC (1024B)
- ✔Throughput: FW + AVC + IPS (1024B)
Bulk pricing available · Export packing & documentation · DHL / FedEx / air / sea freight
Technical Specifications
| Features | 4112 |
|---|---|
| Throughput: FW + AVC (1024B) | 19 Gbps |
| Throughput: FW + AVC + IPS (1024B) | 19 Gbps |
| Maximum concurrent sessions, with AVC | 10 million |
| Maximum new connections per second, with AVC | 98K |
| TLS (Hardware Decryption) 1 | 4.5 Gbps |
| Throughput: NGIPS (1024B) | 19 Gbps |
| IPSec VPN Throughput (1024B TCP w/Fastpath) | 8.5 Gbps |
| Maximum VPN Peers | 10,000 |
| Multi-Instance Capable | Yes |
| Centralized management | Centralized configuration, logging, monitoring, and reporting are performed by the Management Center or alternatively in the cloud with Cisco Defense Orchestrator |
| Application Visibility and Control (AVC) | Standard, supporting more than 6000 applications, as well as geolocations, users, and websites |
| AVC: OpenAppID support for custom, open source, application detectors | Standard |
| Cisco Security Intelligence | Standard, with IP, URL, and DNS threat intelligence |
| Cisco Secure IPS License | Available; can passively detect endpoints and infrastructure for threat correlation and Indicators of Compromise (IoC) intelligence |
| Cisco Malware Defense for Networks | Available; enables detection, blocking, tracking, analysis, and containment of targeted and persistent malware, addressing the attack continuum both during and after attacks. Integrated threat correlation with Cisco Secure Endpoint is also optionally available |
| Cisco Malware Analytics sandboxing | Available |
| URL filtering: number of categories | More than 120 |
| URL filtering: number of URLs categorized | More than 280 million |
| Third-party and open-source ecosystem | Open API for integrations with third-party products; Snort ® and OpenAppID community resources for new and specific threats |
| High availability | Cisco Secure Firewall 4100 Series with Firepower Threat Defense in HA configuration supports Active/Standby setup. This is available at the appliance level or logical instances defined on two different appliances. Please check latest High Availability Configuration Guide chapter for guidelines and best practices. |
| Clustering | Cisco Secure Firewall 4100 Series with Firepower Threat Defense allows clustering of up to 16 appliances, or up to 16 instances across different appliances running Multi Instance feature. Clustering allows to increase overall performance and scale. Please check latest Clustering Configuration Guide chapter for guidelines and best practices. |
| Cisco Trust Anchor Technologies | Cisco Secure Firewall 4100 Series platforms include Trust Anchor Technologies for supply chain and software image assurance |
Product Overview
The Cisco Secure Firewall 4100 Series is a family of four threat-focused NGFW security platforms. Their throughput range addresses internet edge, data center and service provider use cases. They deliver superior threat defense, at faster speeds, with a smaller footprint. Cisco Secure Firewall 4100 Series supports flow-offloading, programmatic orchestration, and the management of security services with RESTful APIs. Network Equipment Building Standards (NEBS)-compliance is supported by the Cisco Secure Firewall 4125 platform. The 4100 Series platforms can run either the Cisco Secure Firewall ASA or Cisco Secure Firewall Threat Defense (FTD) software.
Centralized configuration, logging, monitoring, and reporting are performed by the Management Center or alternatively in the cloud with Cisco Defense Orchestrator
Available; enables detection, blocking, tracking, analysis, and containment of targeted and persistent malware, addressing the attack continuum both during and after attacks. Integrated threat correlation with Cisco Secure Endpoint is also optionally available
Cisco Secure Firewall 4100 Series with Firepower Threat Defense in HA configuration supports Active/Standby setup. This is available at the appliance level or logical instances defined on two different appliances. Please check latest High Availability Configuration Guide chapter for guidelines and best practices.
Cisco Secure Firewall 4100 Series with Firepower Threat Defense allows clustering of up to 16 appliances, or up to 16 instances across different appliances running Multi Instance feature. Clustering allows to increase overall performance and scale. Please check latest Clustering Configuration Guide chapter for guidelines and best practices.
Related Network Firewalls
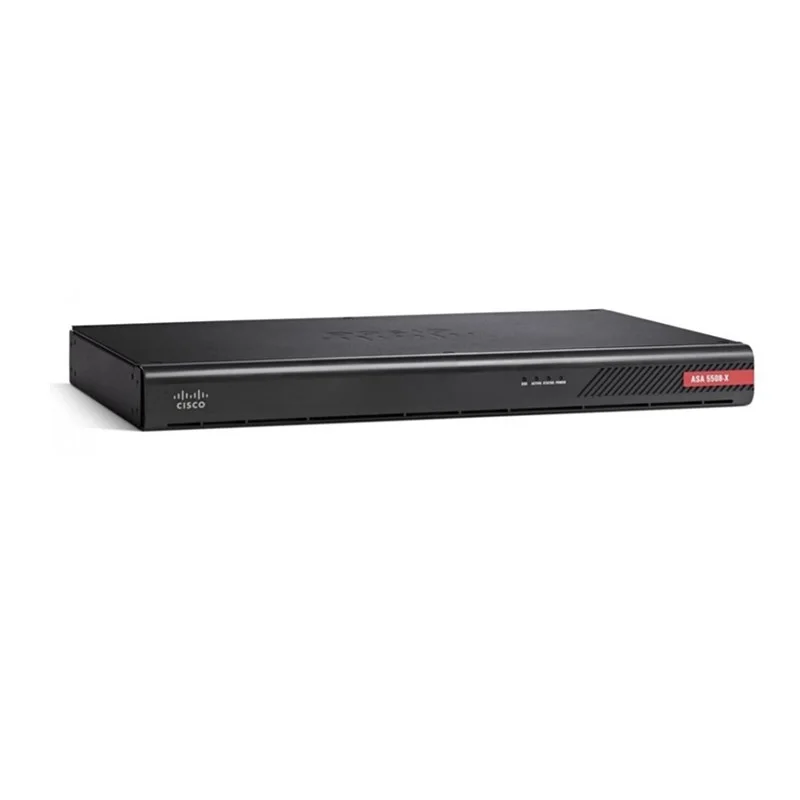
Cisco
ASA5508-K9
New Original Cisco ASA5508-K9 ASA 5508-X Network Security Firewall
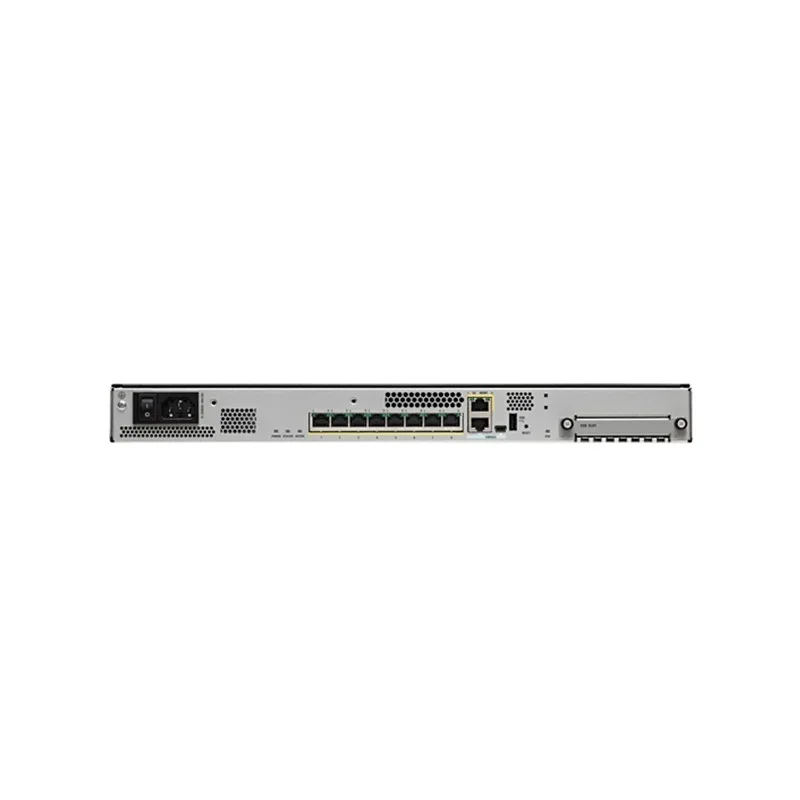
Cisco
ASA5516-FPWR-K9
New Original ASA5516-FPWR-K9 ASA 5516-X Network Security Firewall

Cisco
ASA5525-FPWR-K9
New Original ASA5525-FPWR-K9 ASA 5525-X Network Security Firewall
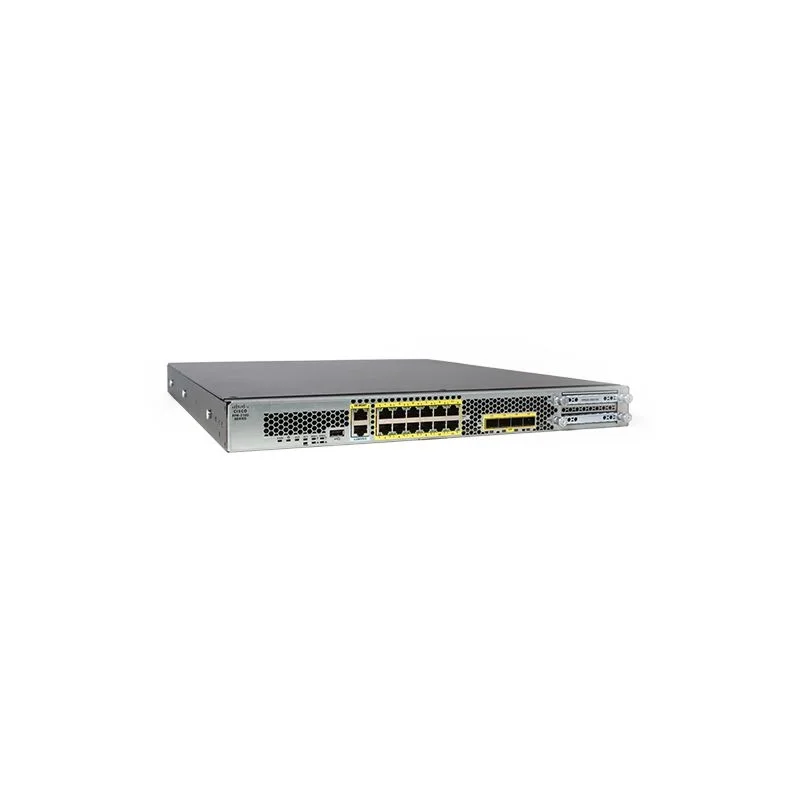
Cisco
FPR2130-ASA-K9
Cisco FPR2130-ASA-K9 Network Firewalls
Cisco
FPR2K-SSD100
FPR2K-SSD100 FPR2K-SSD100 - Cisco Firepower 2100 Series
About Network Firewalls from ImportGM
Next-generation firewalls and security gateways from Fortinet FortiGate, Cisco ASA/Firepower and H3C, covering branch SMB to data-centre throughput classes.
Browse all Network Firewalls →