
H3C · Network Firewall
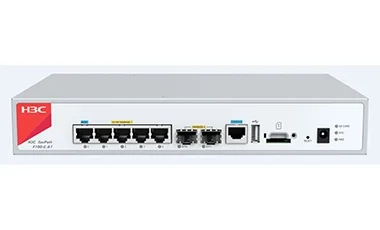
H3C SecPath F100-C-A1 Firewalls Enterprises Network Integration Firewalls
Model: F100-C-A1|Condition: Original New|Warranty: 1 year
ImportGM lists the H3C F100-C-A1 as a regular stock line for international resellers, MSPs and rollout projects that need genuine network firewalls. Use H3C highly available proprietary software and hardware platforms that have been proven by Telecom carriers and small- to medium-sized enterprises. Core parameters include ports 5 × GE + 2 × SFP (MTU: 1500 defaultly), storage media TF card with a maximum size of 500 GB. Original New units carry the 1 year ImportGM warranty; quotation, proforma invoice and export packing list are issued the same day.
- ✔High-performance software and hardware processing platform
- ✔F100-C-A1 and F100-C-A2 use advanced 64-bit multi-core high-performance processors and caches.
- ✔Carrier-level high availability
- ✔Powerful security protection features
- ✔Security zone—Allows you to configure security zones based on interfaces and VLANs.
- ✔Access control—Supports access control based on users and applications and integrates deep intrusion prevention with access control.
Bulk pricing available · Export packing & documentation · DHL / FedEx / air / sea freight
Technical Specifications
| Size (WxDxH) | 266mmx161mmx44mm |
|---|---|
| Ports | 5 × GE + 2 × SFP (MTU: 1500 defaultly) |
| Storage media | TF card with a maximum size of 500 GB |
| Ambient temperature | Operating: 0°C to 45°C (32°F to 113°F) Storage: –40°C to +70°C (–40°F to +158°F) |
| Operating mode | Route, transparent, or hybrid |
| AAA | Portal authentication RADIUS authentication HWTACACS authentication PKI/CA (X.509 format) authentication Domain authentication CHAP authentication PAP authentication |
| Firewall | SOP virtual firewall technology, which supports full virtualization of hardware resources, including CPU, memories, and storage Security zone Attack protection against malicious attacks, such as land, smurf, fraggle, ping of death, teardrop, IP spoofing, IP fragmentation, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, address/port scanning, SYN flood, ICMP flood, UDP flood, and DNS query flood Basic and advanced ACLs Time range-based ACL User-based and application-based access control ASPF application layer packet filtering Static and dynamic blacklist function MAC-IP binding MAC-based ACL 802.1Q VLAN transparent transmission Sub-Interface VLAN |
| Antivirus | Signature-based virus detection Manual and automatic upgrade for the signature database Stream-based processing Virus detection based on HTTP, FTP, SMTP, and POP3 Virus types include Backdoor, Email-Worm, IM-Worm, P2P-Worm, Trojan, AdWare, and Virus Virus logs and reports |
| Deep intrusion prevention | Prevention against common attacks such as hacker, worm/virus, Trojan, malicious code, spyware/adware, DoS/DDoS, buffer overflow, SQL injection, and IDS/IPS bypass Attack signature categories (based on attack types and target systems) and severity levels (including high, medium, low, and notification) Manual and automatic upgrade for the attack signature database (TFTP and HTTP). P2P/IM traffic identification and control |
| Email/webpage/ application layer filtering | Email filtering SMTP email address filtering Email subject/content/attachment filtering Webpage filtering HTTP URL/content filtering Java blocking ActiveX blocking SQL injection attack prevention |
| NAT | Many-to-one NAT, which maps multiple internal addresses to one public address Many-to-many NAT, which maps multiple internal addresses to multiple public addresses One-to-one NAT, which maps one internal address to one public address NAT of both source address and destination address External hosts access to internal servers Internal address to public interface address mapping NAT support for DNS Setting effective period for NAT NAT ALGs for NAT ALG, including DNS, FTP, H.323, ILS, MSN, NBT, PPTP, and SIP |
| VPN | L2TP VPN IPSec VPN GRE VPN SSL VPN |
| IP Services | IP Forwarding ICMP, Tracert, ping, Telnet, DHCP Server, DCHP Relay, and DHCP Client Routing: Static, RIP, OSPF, BGP Multicast: IGMP, PIM-SM and PIM-DM VRRP IPv6 status firewall IPv6 attack protection IPv6 forwarding IPv6 protocols such as ICMPv6, PMTU, Ping6, DNS6, TraceRT6, Telnet6, DHCPv6 Client, and DHCPv6 Relay IPv6 routing: RIPng, OSPFv3, BGP4+, static routing, policy-based routing IPv6 multicast: PIM-SM, and PIM-DM IPv6 transition techniques: NAT-PT, IPv6 tunneling, NAT64 (DNS64), and DS-LITE IPv6 security: NAT-PT, IPv6 tunnel, IPv6 packet filter, RADIUS, IPv6 zone pair policies, IPv6 connection limit |
| Encryption algorithm | MD5/SHA1/SHA256/SHA384/SHA512/SM3/3DES-CBC/AES-CBC-128/ AES-CBC-192/ AES-CBC-256/DES-CBC/SM1-CBC-128/SM4-CBC |
| Configuration management | CLI Configuration management via console port Remote management through Web, SSH Device management through H3C IMC SSM SNMPv3, compatible with SNMPv2 and SNMPv1 Intelligent security policy |
| Environmental protection | EU RoHS compliance |
| EMC | EN 55032 ClassA VCCI-CISPR 32 ClassA FCC Part 15 Subpart B ClassA AS/NZS CISPR32 ClassA ICES-003 ClassA ETSI EN 300 386 EN 61000-3-2 EN 61000-3-3 EN 55035 |
| Safety | GB 4943.1 UL 62368-1 CAN/CSA C22.2 No 62368-1 IEC 62368-1 EN 62368-1 AS/NZS 62368-1 FDA 21 CFR Subchapter J |
Product Overview
Use H3C highly available proprietary software and hardware platforms that have been proven by Telecom carriers and small- to medium-sized enterprises.
Support H3C SCF, which can virtualize multiple devices into one device for unified resources management, service backup, and system performance improvement.
Attack protection—Detects and prevents various attacks, including Land, Smurf, Fraggle, ping of death, Tear Drop, IP spoofing, IP fragment, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, IP/port scanning, and common DDoS attacks such as SYN flood, UDP flood, DNS flood, and ICMP flood.
Packet filtering—Allows you to apply standard or advanced ACLs between security zones to filter packets based on information contained in the packets, such as UDP and TCP port numbers. You can also configure time ranges during which packet filtering will be performed.
ASPF—Dynamically determines whether to forward or drop a packet by checking its application layer protocol information and state. ASPF supports inspecting FTP, HTTP, SMTP, RTSP, and other TCP/UDP-based application layer protocols.
Attack protection against malicious attacks, such as land, smurf, fraggle, ping of death, teardrop, IP spoofing, IP fragmentation, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, address/port scanning, SYN flood, ICMP flood, UDP flood, and DNS query flood
Related Network Firewalls
H3C
F100-C-A2
H3C SecPath F100-C-A2 Firewalls Enterprises Network Integration Firewalls
Cisco
ASA5508-K9
New Original Cisco ASA5508-K9 ASA 5508-X Network Security Firewall
Cisco
ASA5516-FPWR-K9
New Original ASA5516-FPWR-K9 ASA 5516-X Network Security Firewall

Cisco
ASA5525-FPWR-K9
New Original ASA5525-FPWR-K9 ASA 5525-X Network Security Firewall
Cisco
FPR2130-ASA-K9
Cisco FPR2130-ASA-K9 Network Firewalls
About Network Firewalls from ImportGM
Next-generation firewalls and security gateways from Fortinet FortiGate, Cisco ASA/Firepower and H3C, covering branch SMB to data-centre throughput classes.
Browse all Network Firewalls →