
Cisco · Network Firewall
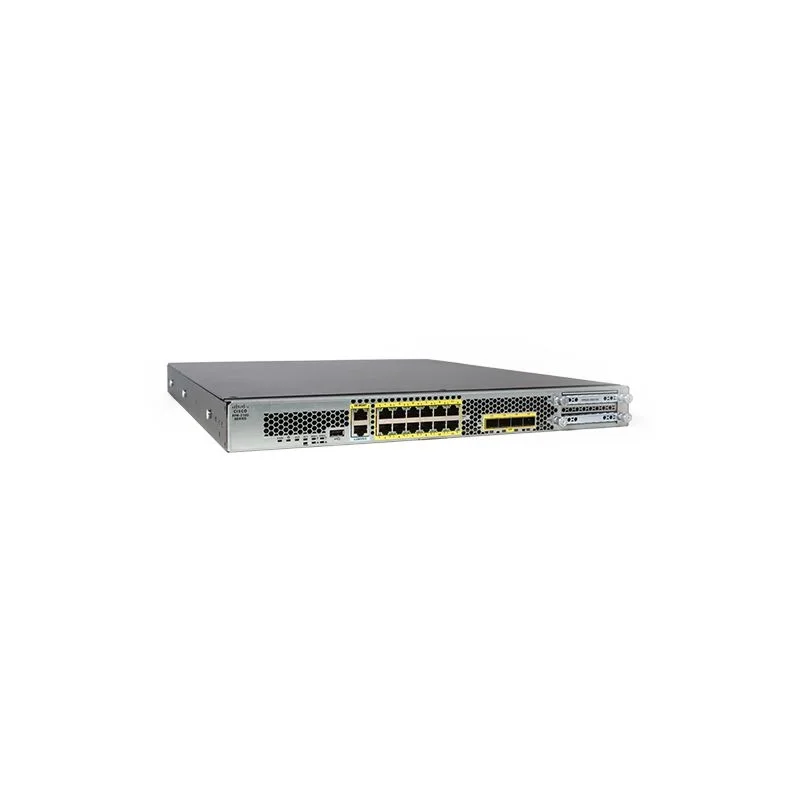
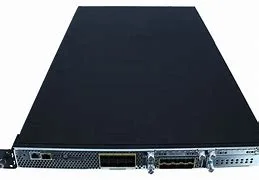
Cisco FPR2130-ASA-K9 Network Firewalls
Model: FPR2130-ASA-K9|Condition: Original Used|Warranty: 3 months
Cisco FPR2130-ASA-K9 — a network firewall shipped from ImportGM's Shenzhen warehouse to channel partners, integrators and corporate IT departments worldwide. Centralized configuration, logging, monitoring, and reporting are performed by Cisco Security Manager or alternatively in the cloud with Cisco Defense Orchestrator. Core parameters include stateful inspection firewall throughput 10 Gbps, stateful inspection firewall throughput (multiprotocol) 5 Gbps. Original Used units carry the 3 months ImportGM warranty; quotation, proforma invoice and export packing list are issued the same day.
- ✔The quick spec.
- ✔Cisco Firepower 2130 ASA Appliance, 1RU,1 x Network Module Bays
- ✔ASA Performance and Capabilities on Firepower Appliances
- ✔Stateful inspection firewall throughput
- ✔Stateful inspection firewall throughput (multiprotocol)
- ✔Concurrent firewall connections
Bulk pricing available · Export packing & documentation · DHL / FedEx / air / sea freight
Technical Specifications
| Product Number | FPR2130-ASA-K9 |
|---|---|
| Product Description | Cisco Firepower 2130 ASA Appliance, 1RU, 1 x Network Module Bays |
| Stateful inspection firewall throughput | 10 Gbps |
| Stateful inspection firewall throughput (multiprotocol) | 5 Gbps |
| Concurrent firewall connections | 2 million |
| New connections per second | 40000 |
| IPsec VPN throughput (450B UDP L2L test) | 1 Gbps |
| IPsec/Cisco AnyConnect/Apex site-to-site VPN peers | 7500 |
| Maximum number of VLANs | 750 |
| Security contexts (included; maximum) | 2; 30 |
| High availability | Active/active and active/standby |
| Scalability | VPN Load Balancing |
| Centralized management | Centralized configuration, logging, monitoring, and reporting are performed by Cisco Security Manager or alternatively in the cloud with Cisco Defense Orchestrator |
| Adaptive Security Device Manager | Web-based, local management for small-scale deployments |
| Dimensions (H x W x D) | 1.73 x 16.90 x 19.76 in. (4.4 x 42.9 x 50.2 cm) |
| Form factor (rack units) | 1RU |
| I/O module slots | 1 NM slot |
| Integrated I/O | 12 x 10M/100M/1GBASE-T Ethernet interfaces (RJ-45), 4 x 10 Gigabit (SFP+) Ethernet interfaces |
| Network modules | (FPR-NM-8X10G) 8 x 10 Gigabit Ethernet Enhanced Small Form-Factor Pluggable (SFP+) network module |
| Maximum number of interfaces | Up to 24 total Ethernet ports (12x1G RJ-45, 4x10G SFP+, and network module with 8x10G SFP+) |
| Integrated network management ports | 1 x 10M/100M/1GBASE-T Ethernet port (RJ-45) |
| Serial port | 1 x RJ-45 console |
| USB | 1 x USB 2.0 Type-A (500mA) |
| Storage | 1x 200 GB, 1x spare slot (for MSP) |
| Power supplies | Configuration |
| AC input voltage | 100 to 240V AC |
| AC maximum input current | < 6A at 100V |
| AC maximum output power | 400W |
| AC frequency | 50 to 60 Hz |
| AC efficiency | >89% at 50% load |
| DC input voltage | -48V to -60VDC |
| DC maximum input current | < 12.5A at -48V |
| DC maximum output power | 350W |
| DC efficiency | >88% at 50% load |
| Redundancy | 1+1 AC or DC with dual supplies |
| Fans | 1 hot-swappable fan module (with 4 fans) |
| Noise | 56 dBA @ 25C 77 dBA at highest system performance. |
| Rack mountable | Yes. Mount rails included (4-post EIA-310-D rack) |
| Weight | 19.4 lb (8.8 kg) 1 x power supplies, 1 x NM, 1 x fan module, 2x SSDs |
| Temperature: operating | 32 to 104 ° F (0 to 40 ° C) or NEBS operation (see below) |
| Temperature: nonoperating | -4 to 149°F (-20 to 65°C) |
| Humidity: operating | 10 to 85% noncondensing |
| Humidity: nonoperating | 5 to 95% noncondensing |
| Altitude: operating | 10,000 ft (max) or NEBS operation (see below) |
| Altitude: nonoperating | 40,000 ft (max) |
| NEBS operation | Operating altitude: 0 to 13,000 ft (3962 m) Operating temperature: Long term: 0 to 45 ° C, up to 6,000 ft (1829 m) Long term: 0 to 35 ° C, 6,000 to 13,000 ft (1829 to 3964 m) Short term: -5 to 55 ° C, up to 6,000 ft (1829 m) |
Product Overview
Centralized configuration, logging, monitoring, and reporting are performed by Cisco Security Manager or alternatively in the cloud with Cisco Defense Orchestrator
Cisco Firepower Threat Defense (FTD) is an integrative software image combining CISCO ASA and FirePOWER feature into one hardware and software inclusive system. ... there is only FTD software.wich can be managed through Cisco FMC a single management console to manage an entire platform.
FirePower 2100 series provide 4 platforms: Firepower 2110 (Up to 2.0 Gbps, Multiservice capable, 12 x 1 GE fixed, 4 SFP (1 GE) ports, 1RU), Firepower 2120 (Up to 3 Gbps, Multiservice capable, 12 x 1 GE fixed, 4 SFP (1 GE) ports, 1RU), Firepower 2130 (Up to 5 Gbps, Multiservice capable, Up to 24 x 1 GE or 12 X 1GE and 12x10GE ports, 1RU), and Firepower 2140 (Up to 8.5 Gbps, Multiservice capable, Up to 24 x 1 GE or 12 X 1GE and 12x10GE ports, 1RU).
The Cisco Firepower® NGFW (next-generation firewall) is the industry's first fully integrated, threat-focused next-gen firewall with unified management. It uniquely provides advanced threat protection before, during, and after attacks.
1. Threat-focused NGFW : Improve business resiliency and maintain performance with superior threat defense. Apply granular application control. Protect against malware. Shrink time to detection and remediation. Reduce complexity with the on-device management interface. 2. Optimized performance and port density : Firewall throughput speeds from 2 Gbps to 8.5 Gbps. Support for sixteen (16) 1 GE ports on the low-end models. The high-end models support up to twenty-four (24) 1 GE ports or up to twelve (12) 10 GE ports. All in a 1RU form factor. 3. Innovative architecture : With its unique dual-CPU, multicore architecture, the 2100 maintains throughput performance when threat inspection is activated by routing different workloads to different chips. And enabling the threat protection features does not affect the firewall throughput. 4. Integration adds value : Further strengthen your defenses. Share intelligence, context, and policy controls by integration with third-party and other Cisco security solutions. Enable automatic device quarantining and rapid threat containment with Cisco ISE. 5. Management to meet your needs : Cisco Firepower NGFW is now even less time-consuming to configure and less costly to manage. You can choose from local, centralized, and cloud-based managers that fit your environment and the way you work.
Related Network Firewalls
Cisco
ASA5508-K9
New Original Cisco ASA5508-K9 ASA 5508-X Network Security Firewall
Cisco
ASA5516-FPWR-K9
New Original ASA5516-FPWR-K9 ASA 5516-X Network Security Firewall

Cisco
ASA5525-FPWR-K9
New Original ASA5525-FPWR-K9 ASA 5525-X Network Security Firewall
Cisco
FPR2K-SSD100
FPR2K-SSD100 FPR2K-SSD100 - Cisco Firepower 2100 Series
Cisco
FPR4110-ASA-K9
Cisco Firepower 4100 Series FPR4110-ASA-K9
About Network Firewalls from ImportGM
Next-generation firewalls and security gateways from Fortinet FortiGate, Cisco ASA/Firepower and H3C, covering branch SMB to data-centre throughput classes.
Browse all Network Firewalls →