
Cisco · Network Firewall
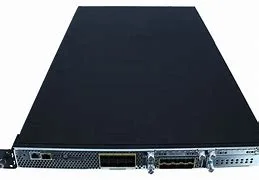
Cisco Firepower 4100 Series FPR4110-ASA-K9
Model: FPR4110-ASA-K9|Condition: Original New|Warranty: 1 year
ImportGM lists the Cisco FPR4110-ASA-K9 as a regular stock line for international resellers, MSPs and rollout projects that need genuine network firewalls. Centralized configuration, logging, monitoring, and reporting are performed by the Management Center or alternatively in the cloud with Cisco Defense Orchestrator. Core parameters include dimensions (h x w x d) 1.75 x 16.89 x 29.7 in. (4.4 x 42.9 x 75.4 cm), form factor (rack units) 1RU. Original New units carry the 1 year ImportGM warranty; quotation, proforma invoice and export packing list are issued the same day.
- ✔Optional Interfaces
- ✔8 x SFP+ on-chassis
- ✔Detailed performance specifications and feature highlights
- ✔Throughput: FW + AVC (1024B)
- ✔Throughput: FW + AVC + IPS (1024B)
- ✔Maximum concurrent sessions, with AVC
Bulk pricing available · Export packing & documentation · DHL / FedEx / air / sea freight
Technical Specifications
| Features | 4112 |
|---|---|
| Dimensions (H x W x D) | 1.75 x 16.89 x 29.7 in. (4.4 x 42.9 x 75.4 cm) |
| Form factor (rack units) | 1RU |
| Supervisor | Cisco Secure Firewall 4000 Supervisor with 8 x 10 Gigabit Ethernet ports and 2 Network Module (NM) slots for I/O expansion |
| Network modules | ● 2 x 100 Gigabit Ethernet QSFP28 Network Module ● 8 x 10 Gigabit Ethernet Enhanced Small Form-Factor Pluggable (SFP+) network modules ◦ 8 x 1 Gbps Fiber or 4 x 1Gbps Copper SFP Network Module ● 4 x 40 Gigabit Ethernet Quad SFP+ network modules ● 8-port 1Gbps copper, FTW (fail to wire) Network Module ◦ Ports that are not configured as FTW can be used as regular 1 Gb copper ports ● 6-port 1 Gbps SX Fiber FTW (fail to wire) Network Module ● 6-port 10Gbps SR Fiber FTW (fail to wire) Network Module ● 6-port 10Gbps LR Fiber FTW (fail to wire) Network Module ● 2-port 40G SR FTW (fail to wire) Network Module ● 2-port 100Gbps Network Module |
| Maximum number of interfaces | Up to 4 x 100 Gigabit Ethernet (QSFP28) interfaces, 24 x 10 Gigabit Ethernet (SFP+) interfaces; up to 8 x 40 Gigabit Ethernet (QSFP+) interfaces with 2 network modules; up to 24 x 1 Gigabit Ethernet ports(SFP) with network modules and fixed ports |
| Integrated network management ports | 1 Gigabit Ethernet SFP port Supports 1Gbps fiber or copper optical modules |
| Serial port | 1 x RJ-45 console |
| USB | 1 x USB 2.0 |
| Storage | 400 GB |
| Power supplies | Configuration |
| AC input voltage | 100 to 240V AC |
| AC maximum input current | 13A |
| AC maximum output power | 1100W |
| AC frequency | 50 to 60 Hz |
| AC efficiency | >92% at 50% load |
| DC input voltage | -40V to -60VDC |
| DC maximum input current | 27A |
| DC maximum output power | 950W |
| DC efficiency | >92.5% at 50% load |
| Redundancy | 1+1 |
| Fans | 6 hot-swappable fans |
| Noise | Typical 63 dBA, max is 74 dBA |
| Rack mountable | Yes, mount rails included (4-post EIA-310-D rack) |
| Weight | 4112/4115/4125/4145: 39.4 lb (17.87 kg) 2 x power supplies, 2 x NMs, 6 x fans; 31.4 lb (14.24 kg) no power supplies, no NMs, no fans |
| Temperature: operating | 32 to 104°F (0 to 40°C) |
| Temperature: nonoperating | -40 to 149°F (-40 to 65°C) |
| Humidity: operating | 5 to 95% noncondensing |
| Humidity: nonoperating | 5 to 95% noncondensing |
| Altitude: operating | 10,000 ft (max) |
| Altitude: nonoperating | 40,000 ft (max) |
| NEBS operation (FPR 4125 only) | Operating altitude: 0 to 13,000 ft (3960 m) Operating temperature: Long term: 0 to 45°C, up to 6,000 ft (1829 m) Long term: 0 to 35°C, 6,000 to 13,000 ft (1829 to 3964 m) Short term: -5 to 50°C, up to 6,000 ft (1829 m) |
Product Overview
Centralized configuration, logging, monitoring, and reporting are performed by the Management Center or alternatively in the cloud with Cisco Defense Orchestrator
Available; enables detection, blocking, tracking, analysis, and containment of targeted and persistent malware, addressing the attack continuum both during and after attacks. Integrated threat correlation with Cisco Secure Endpoint is also optionally available
Cisco Secure Firewall 4100 Series with Firepower Threat Defense in HA configuration supports Active/Standby setup. This is available at the appliance level or logical instances defined on two different appliances. Please check latest High Availability Configuration Guide chapter for guidelines and best practices.
Cisco Secure Firewall 4100 Series with Firepower Threat Defense allows clustering of up to 16 appliances, or up to 16 instances across different appliances running Multi Instance feature. Clustering allows to increase overall performance and scale. Please check latest Clustering Configuration Guide chapter for guidelines and best practices.
Note: Performance will vary depending on features activated, and network traffic protocol mix, and packet size characteristics. Performance is subject to change with new software releases. Consult your Cisco representative for detailed sizing guidance.
Active/active or active/standby. Active/active is only available with multiple contexts configured. Please check latest Failover for High Availability Configuration Guide chapter for guidelines and best practices.
Related Network Firewalls
Cisco
ASA5508-K9
New Original Cisco ASA5508-K9 ASA 5508-X Network Security Firewall
Cisco
ASA5516-FPWR-K9
New Original ASA5516-FPWR-K9 ASA 5516-X Network Security Firewall

Cisco
ASA5525-FPWR-K9
New Original ASA5525-FPWR-K9 ASA 5525-X Network Security Firewall
Cisco
FPR2130-ASA-K9
Cisco FPR2130-ASA-K9 Network Firewalls
Cisco
FPR2K-SSD100
FPR2K-SSD100 FPR2K-SSD100 - Cisco Firepower 2100 Series
About Network Firewalls from ImportGM
Next-generation firewalls and security gateways from Fortinet FortiGate, Cisco ASA/Firepower and H3C, covering branch SMB to data-centre throughput classes.
Browse all Network Firewalls →