
H3C · Network Router
H3C CR16006-F High-end Data Center SDN/BRAS Support High-Speed Enterprise Router
Model: CR16006-F|Condition: Original New|Warranty: 1 year
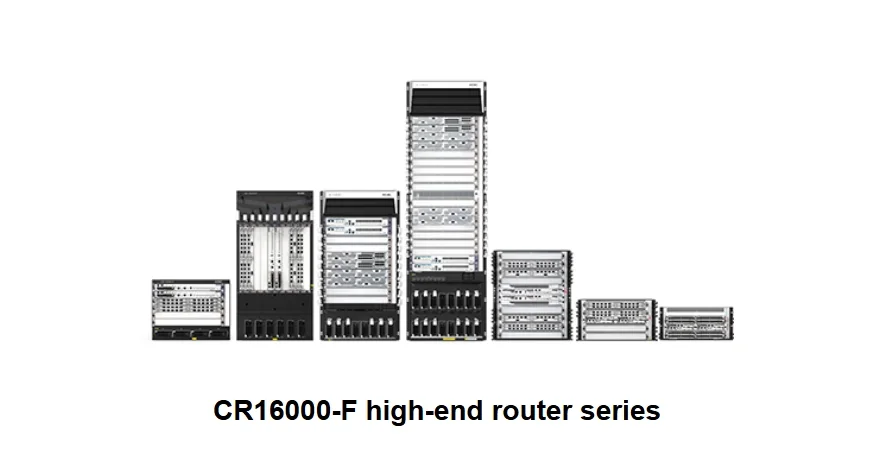
ImportGM lists the H3C CR16006-F as a regular stock line for international resellers, MSPs and rollout projects that need genuine network routers. The CR16000-F is a high-end router series independently developed by H3C. It utilizes distributed hardware forwarding, and non-blocking switching technology. It adopts an advanced CLOS architecture with a separate control plane and forwarding plane. Core parameters include switching capacity 6.4T, forwarding performance 1,449.60 Mpps. Original New units carry the 1 year ImportGM warranty; quotation, proforma invoice and export packing list are issued the same day.
- ✔Comprehensive SDN capabilities
- ✔Supports SR/SRv6+EVPN technology, simplifying network configuration and achieving manageable and controllable network paths.
- ✔Supports EVPN/VXLAN, learning MAC addresses and routing information remotely to implement Layer 2 and Layer 3 VPN based on VXLAN.
- ✔Powerful BRAS functions
- ✔Supports BRAS IRF hot backup, avoiding single point of failures while simplifying operations, maintenance, and management.
- ✔Mobile carrier network IP RAN
Bulk pricing available · Export packing & documentation · DHL / FedEx / air / sea freight
Technical Specifications
| Switching Capacity | 6.4T |
|---|---|
| Forwarding Performance | 1,449.60 Mpps |
| Maximum Board capacity | 1.6T |
| MPU slots | 2 (1+1 redundancy) |
| Subcard slots | 8 |
| Line card slots | 2 |
| Switch fabric modules | 2 (1+1 redundancy) |
| Total number of slots (LPUs + MPUs + independent switch fabric modules) | 4 |
| Chassis | Integrated chassis, which can be installed in a 19-inch rack |
| Power module system | 4 × AC or DC power supplies (N+M redundancy) and built-in AC power supplies |
| Dimensions (H × W × D) | 219mm×440mm ×600mm(8.62×17.32 ×23.70 in) (5RU) |
| Weight in Full Configuration | <70 kg (154.32 lb) |
| Interface types | FE, GE, 10-GE (LAN/WAN), 25-GE, 40-GE, 50-GE, 100-GE, 400-GE, 155M POS, 622M POS, 2.5G POS, 10G POS, CPOS, 155M ATM, 622M ATM, E1/T1 400-GE to 100-GE interface switching 100-GE to 40-GE interface switching 155M POS, 622M POS, and GE interface switching ATM to POS interface switching 155M ATM to 622M ATM interface switching |
| Unicast routing | IPv4/IPv6 dual stack Static routing, RIP, RIPv2, RIPng, OSPF, OSPFv3, IS-IS, IS-ISv6, BGP, BGP4+, and MP-BGP DHCP Server, DHCP Relay VRRP and VRRPv3 IPv6 neighbor discovery, PMTU discovery, TCP6, ping IPv6, traceroute IPv6, socket IPv6, static IPv6 DNS, specifying an IPv6 DNS server, and TFTP IPv6 client ICMPv6 MIB, UDP6 MIB, TCP6 MIB, and IPv6 MIB ECMP/UCMP Policy-based routing Routing policies Tunneling technologies such as GRE FRR for static routing, OSPF, IS-IS, BGP, and OSPFv3 Filtering routes based on IP address, AS path, and route tag |
| Multicast | Routing protocols such as PIM-DM, PIM-SM, PIM-SSM, MSDP, MBGP, and anycast-RP IGMP v1/v2/v3 and IGMP snooping v1/v2/v3 IGMP Proxy and Snooping PIM6-DM, PIM6-SM, and PIM6-SSM MLD v1/v2 and MLD snooping v1 Multicast policies and multicast QoS BIER |
| MPLS VPN | MPLS label distribution protocols such as LDP and RSVP-TE, and LDP label capacity greater than 512K P/PE functions, which comply with RFC2547bis Three inter-AS MPLS VPN methods (Option1/Option2/Option3) Hierarchy of PE (HoPE) Multi-role hosts BGP and LDP L2VPN, L3VPN, VPLS and inter-AS L2VPN/L3VPN EVPN VPLS/VPWS/L3VPN 6PE and 6vPE Distributed multicast VPN ACL-based traffic identification and redirection to different VPNs MPLS VPN troubleshooting features, including MPLS ping and MPLS traceroute L2VPN access to L3VPN VPLS access in QinQ mode MPLS TE FRR and LDP FRR |
| BRAS service | PPPoE, PPPoEoVLAN, and PPPoEoQ access authentication methods PPPoX function, and PPPoA and PPPoEoA access authentication methods Layer 2 portal, Layer 3 portal, and QinQ portal access authentication methods IPoE, IPoEoVLAN, and IPoEoQ access authentication methods Subnet-/interface-/L2VPN-leased access authentication methods L2TP Layer 2 transparent access and Layer 3 transparent access Remote AAA based on RADIUS/TACACS+ RADIUS, TACACS, and COPS protocols Intelligent target accounting (ITA), which differentiates services by destination addresses to perform accounting, bandwidth control, and QoS Unified wired and wireless authentication, which meets the access requirements of massive user endpoints through a high-capacity BRAS and meets the mobility requirements of wireless endpoints BRAS IRF, which offers redundancy and simplifies Ops |
| Value-added services | IPsec on the following types of interfaces: high-speed link interfaces (FE, GE, 10-GE, 40-GE, 50-GE, 100-GE, 2.5G POS, and 10G POS) and low-speed link interfaces (155M POS, 622M POS, CPOS interface, 155M ATM, 622M ATM, and E1/T1) High-precision NAT: Carrier Grade NAT (CGN), Static NAT, Dynamic NAT, NAT44/NAT444, NAT64 1588 V2 |
| Virtualization features | Virtualization technology, which virtualizes multiple physical devices into a logical device, manages devices and forwarding entries on a unified interface, and supports multi-chassis link aggregation |
| ACL | IPv4/IPv6 standard ACLs and extended ACLs Layer 2/Layer 3/Layer 4-based ACLs Ingress/Egress ACLs Hardware ACLs |
| QoS | Hierarchical QoS (HQoS) and queue scheduling mechanisms such as PQ, WFQ, and CBWFQ 5-level HQoS scheduling for granular service management Traffic shaping Congestion avoidance technologies such as tail drop (TD) and Weighted Random Early Detection (WRED) Priority marking/remarking, and 802.1p, ToS, DSCP, and EXP priority mappings Congestion avoidance, traffic policing (CAR), and traffic shaping Packet marking based on IP address, port number, 802.1p priority, and DSCP value Multi-level queue scheduling mechanisms (including CQ, PQ, LLQ, and WFQ) for packets Multicast QoS QPPB, and QoS for MPLS TE |
| Ethernet | 802.1Q, VLAN Ethernet Virtual Circuits ( EVC) Layer2ProtocolTunneling 802.1Q VLAN trunk QinQ VLAN encapsulation QinQ termination 802.3d (STP), 802.3w (RSTP), and 802.3s (MSTP) IEEE 802.3ad (link aggregation), static link aggregation, and multi-card link aggregation Aggregation of interfaces at different rates Port mirroring (SPAN/RSPAN) and flow mirroring MACsec FlexE Subinterface channelization (slicing) On-demand channelization (slicing) |
| SDN | VXLAN Layer 2 gateway and VXLAN Layer 3 gateway (distributed and centralized) EVPN VXLAN Layer 2 gateway and EVPN VXLAN Layer 3 gateway (distributed and centralized) PCEP Network information collection protocols such as BGP-LS NETCONF and YANG SR-BE, SR-TE and SR Policy, SR TI-LFA/Anti-micro-loop SRv6-BE, SRv6 TE policy CBTS OpenFlow v1.3 BGP FlowSpec Telemetry APN6 OSPFv3 over SRv6 and IS-IS over SRv6 L2VPN over SRv6, EVPN VPWS over SRv6 policy, and EVPN VPLS over SRv6 policy Color-based traffic steering and DSCP-based traffic steering by SRv6-TE policy Optimization capabilities based on latency, bandwidth, and packet loss rate by SRv6 policy Switchover to SRv6 BE path upon SRv6 policy path failure EVPN E-tree over SRv6 EVPN VPLS over SRv6 policy SR-MPLS BE, SR-MPLS TE, and SR-MPLS TE policy Ping, trace, and traffic statistics collection based on SR/SRv6 TE policy paths, and ping and trace based on SR BE 10 layers of SIDs in the header for SRv6 TE policy without affecting forwarding capabilities |
| Network flow analysis | NetStream, which supports the v5/v8/v9 data export formats, sampling, and flow statistics collection Multiple log hosts Hardware-based network traffic application analysis IPv4/IPv6/MPLS traffic collection and analysis Traffic collection and analysis in the inbound and outbound directions of interfaces Abnormal traffic detection and monitoring |
| Availability | Redundant backup for the key components, including the MPUs, switching fabric modules, power supplies, and fans MPU and LPU separation, and module plus submodule design Passive design for the backplane to prevent single point of failure Network processor (NP) architecture design, which prevents services from affecting forwarding capabilities Hot swapping for all components, and hot swapping of switching fabric modules without removing fan modules Intelligent fan rotation speed tuning Built-in DC and AC power supplies, not occupy service slots Stateful failover, NSF, NSR, and GR IP trunk, MP, and Ethernet interface aggregation IP/LDP/VPN/TE/VLL FRR NSR for OSPF/OSPFv3/ISIS/ISISv6/BGP/BGP4+/VRRP/IPv6 VRRP/PIM SM/PIM DM/LDP MPLS L3VPN/6VPE/MPLS TE primary/secondary switchover without packet loss TI-LFA FRR for SRv6 with switchover time no longer than 50ms PW redundancy, MPLS/Ethernet OAM, Y.1731, routing protocol/port/VLAN damping, and other protection mechanisms Hardware-based BFD, which supports fast failure detection for various protocols (with minimum packet interval of 3.3ms) and a failover time of less than 50ms BFD for VRRP, OSPF, IS-IS, BGP, LDP, TE, SR, VRRPv6, OSPFv3, ISISv6, BGP4+, PW(VCCV) Comprehensive FRR features: IP/IPv6/LDP/TE/VPNv4/VPNv6 FRR, with a service switchover time less than 50ms and a network availability of 99.999% RFC2544, which supports automatically sending packets to detect the throughput, delay, jitter, and packet loss rate of links |
| OAM | In-situ flow information telemetry (iFIT), which can detect network failures in real time, troubleshoot the network failures, and implement visible management over performance data TWAMP, MPLS OAM, VRRP, Ethernet OAM (802.3ah, 802.1ag/Y.1731), LLDP, BFD for eth-trunk, Bit error detection |
| Security | Firewall modules High-performance SM-based encryption modules, which support SM2, SM3, and SM4 encryption algorithms AAA security authentication protocols (for example, RADIUS and TACACS+) Control plane attack defense Security authentication and accounting with primary-secondary RADIUS SSHv1/v2/v3, providing a secure encrypted channel for user login Standard and extended ACLs, which filter packets and prevent network attacks Defense against attacks by packets such as ARP, unknown multicast, broadcast, unknown unicast, local subnet route scanning, TCP SYN, packets with TTL 1, PADI, DHCP, portal, and protocol packets PADI, DHCP, and portal attack defense Unicast Reverse Path Forwarding (uRPF), which prevents network attacks based on source address spoofing Plaintext and MD5 authentication for RIPv2, OSPF, IS-IS, BGP, OSPFv3, IS-ISv6, and BGP4+ protocols, and keychain feature that allows different keys to be active based on time ranges Secure network management through SNMPv3 |
| System management | In-band management and out-of-band management CLI-based configuration through console/AUX modem/Telnet/SSH2.0 File upload/download through FTP, TFTP, XMODEM, and SFTP SNMP v1/v2c/v3 RMON v1/v2, which supports groups 1, 2, 3, and 9 NTP clock Network Quality Analyzer (NQA) Failure alarms and automatic recovery DHCP Data logs ICMP Syslog Traceroute Multi-threaded access to devices through Telnet Hot patching to achieve smooth software upgrade |
| Operating temperature: | 0℃ to 45℃ (32°F to 113°F) |
| Regulatory compliance | Directive2014/30/EU EN55032ClassA, EN 55024/EN 55035 EN 60950-1, EN61000-3-2, EN61000-3-3 IEC 60950-1 UL 60950-1 |
Product Overview
The CR16000-F is a high-end router series independently developed by H3C. It utilizes distributed hardware forwarding, and non-blocking switching technology. It adopts an advanced CLOS architecture with a separate control plane and forwarding plane. It supports high-density FE/GE, 10GE, 25GE, 40GE, 50GE, 100GE, 400GE interfaces, with flexible single-slot performance expansion to meet different network position requirements. It supports the advanced Comware 7 network operating system, which perfectly integrates with the CR16000-F in multiple aspects such as multi-core CPU support, distributed computing, modular design, high availability architecture, virtualization, and openness. It uses mature virtualization technology to improve network reliability while reducing device maintenance workload. It supports powerful BRAS functionality and carrier-grade CGN, meeting the development needs of multi-service edge MSE devices for operators and core devices for campus networks. It supports various network protection technologies and 1588v2 synchronous Ethernet, serving as an ER router to meet the IPRAN networking needs of operators. It supports the SR/SRv6, FlexE, iFIT, and NETCONF technologies, and has comprehensive SDN capabilities. Combined with the AD-WAN controller, it can achieve automatic business distribution, flexible network scheduling, multi-dimensional business assurance, and intelligent network O&M. With the support of IPSec VPN technology, it can meet users' demands for a trusted network.
Supports sub-interface slicing, FlexE, and other hard isolation technologies, reserving broadband resources and ensuring high reliability for high-priority services.
Supports iFIT + Telemetry deep flow detection technology, proactively monitoring network health and transforming passive maintenance into proactive maintenance.
Supports NETCONF and YANG, providing configuration APIs to achieve network configuration automation and accelerate network device and service deployment.
Supports CBTS functionality, selecting different tunnel paths based on different business priorities to achieve differentiated forwarding services.
Supports Intelligent Target Account (iTA), which distinguishes business types by destination address, realizing billing, bandwidth control, and QoS for different types of user businesses, providing users with differentiated business operation solutions.
Related Network Routers
H3C
Aolynk UR105G-P_F
H3C Aolynk UR105G-P_F high-performance enterprise PoE gateway

H3C
Aolynk UR105G-P_FL
H3C Aolynk UR105G-P_FL high-performance enterprise PoE gateway

H3C
Aolynk UR105G-P_FR
H3C Aolynk UR105G-P_FR high-performance enterprise PoE gateway
H3C
Aolynk UR210G-P_F
H3C Aolynk UR210G-P_F high-performance enterprise PoE gateway
H3C
Aolynk UR210G-P_FL
H3C Aolynk UR210G-P_FL high-performance enterprise PoE gateway

H3C
Aolynk UR210G-P_FR
H3C Aolynk UR210G-P_FR high-performance enterprise PoE gateway
About Network Routers from ImportGM
Enterprise routers and SD-WAN edge platforms — Cisco ISR/ASR, Huawei AR/MSR, H3C and MikroTik — for branch, campus WAN and carrier edge.
Browse all Network Routers →